cfm kernsec — Kernel Attack Surface Reduction for Linux
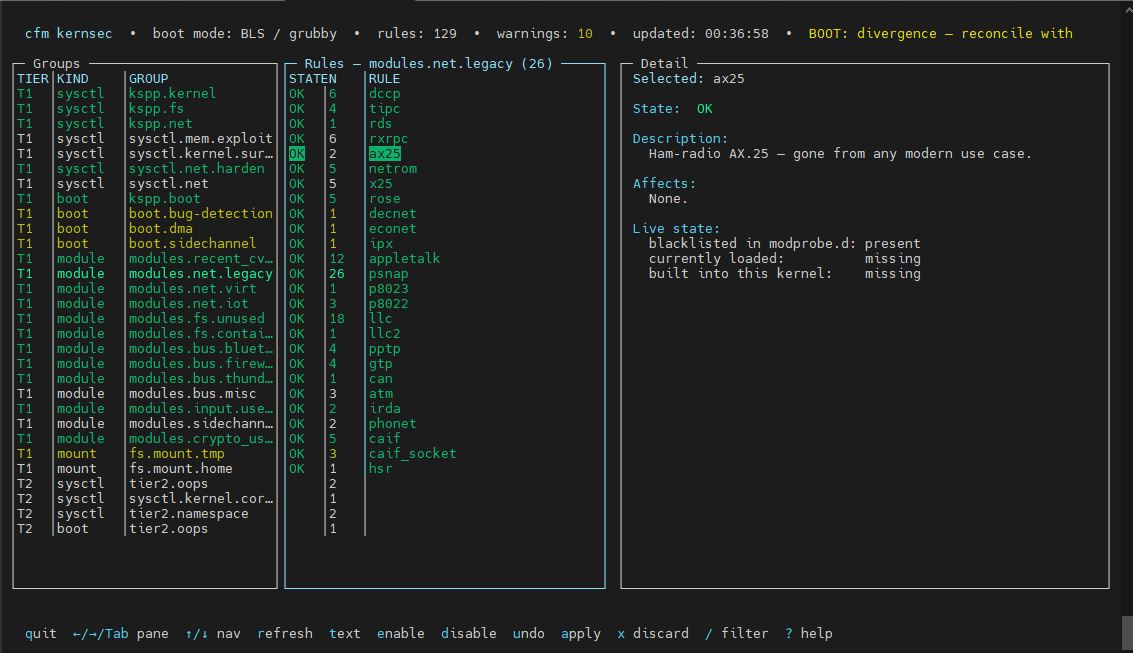
Part of the CFM server security platform. This post covers what kernsec does, how it works, how to use it, and how it relates to the Linux kernel’s proposed Killswitch primitive. The problem it solves A stock AlmaLinux or CloudLinux install ships with a running kernel that supports hundreds of subsystems almost no hosting server … Read more
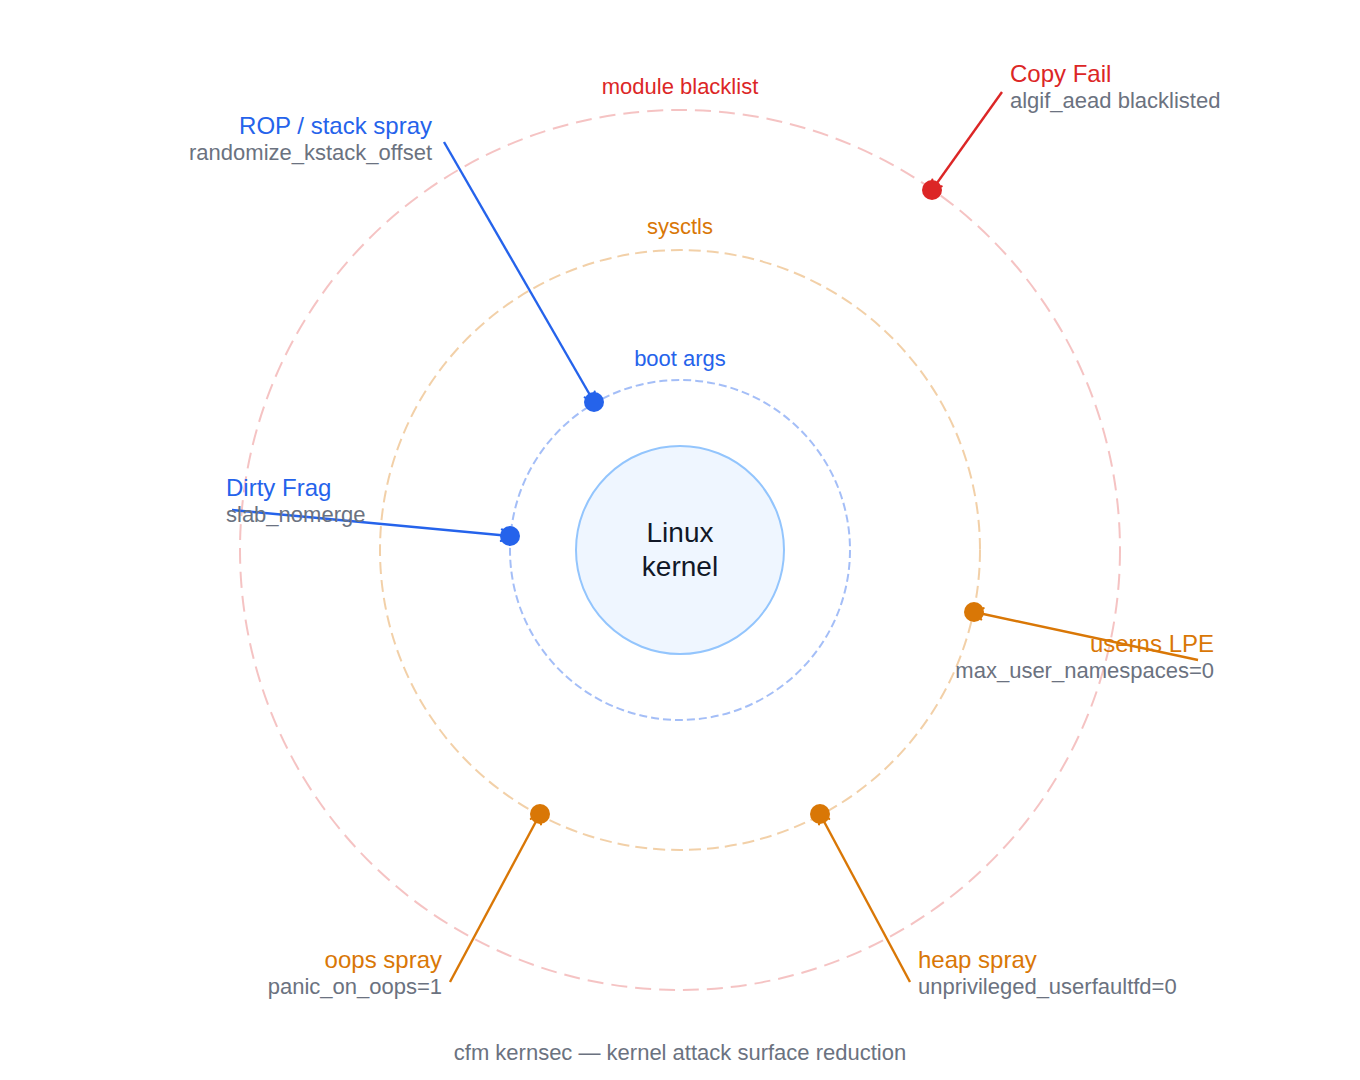
Hardening Shared Linux Hosting Kernels: What cfm kernsec Actually Does (and Doesn’t Do)

A grounded look at kernel attack surface reduction for production hosting servers — no silver bullets, just honest defense. The kernel LPE wave of 2025–2026 was a good reminder that most Linux servers are running with more attack surface exposed than they need. Dirty Frag, Copy Fail (CVE-2026-31431), the ksmbd parade, watch_queue, Dirty Cred — … Read more

CVE-2026-41940: The 64-Day Backdoor Into the Internet’s Control Plane

A critical authentication bypass in cPanel & WHM gave attackers root access to over a million publicly exposed servers — silently, without a password, defeating two-factor authentication — for sixty-four days before anyone patched a thing. What Was Actually at Stake cPanel and WHM are not just web applications. They are the administrative nervous system … Read more