Blesta: Not Everything Should Be Vibe Coded. Apparently, Security Reports Can Be Vibe Ignored.
A WHMCS refugee, two AI assistants, 32 security findings, twelve matching code fixes, and a support ticket that has apparently taken a vow of silence.
sysadmin horror stories
Server and hosting security: CVEs as they land, kernel hardening, WAF rules, malware scanning and responsible disclosure.
A WHMCS refugee, two AI assistants, 32 security findings, twelve matching code fixes, and a support ticket that has apparently taken a vow of silence.
Two critical PHP RCEs, a leaked embargo, a continent of nervous sysadmins, and one daemon that spent the afternoon arguing with its own code reviews. What CFM rules 10021/10022 catch for PHP2Shell (CVE-2026-109618 / CVE-2026-109619) — and what they don’t.
How we stop unmanaged dedicated servers and VMs from adding extra IPs, changing MACs, ARP/NDP spoofing or running rogue DHCP/RA on a shared /24 — with MikroTik raw rules, Cisco Nexus port-security and the Proxmox VE firewall. Verified on production, with the gotchas.
A real-world AlmaLinux 10 SELinux migration from fully disabled to enforcing on a server running Apache, Remi PHP-FPM, BookStack, a Laravel controller, MariaDB, custom SSH port 65535, cron jobs and custom writable paths — with troubleshooting commands and a practical SELinux cheatsheet.
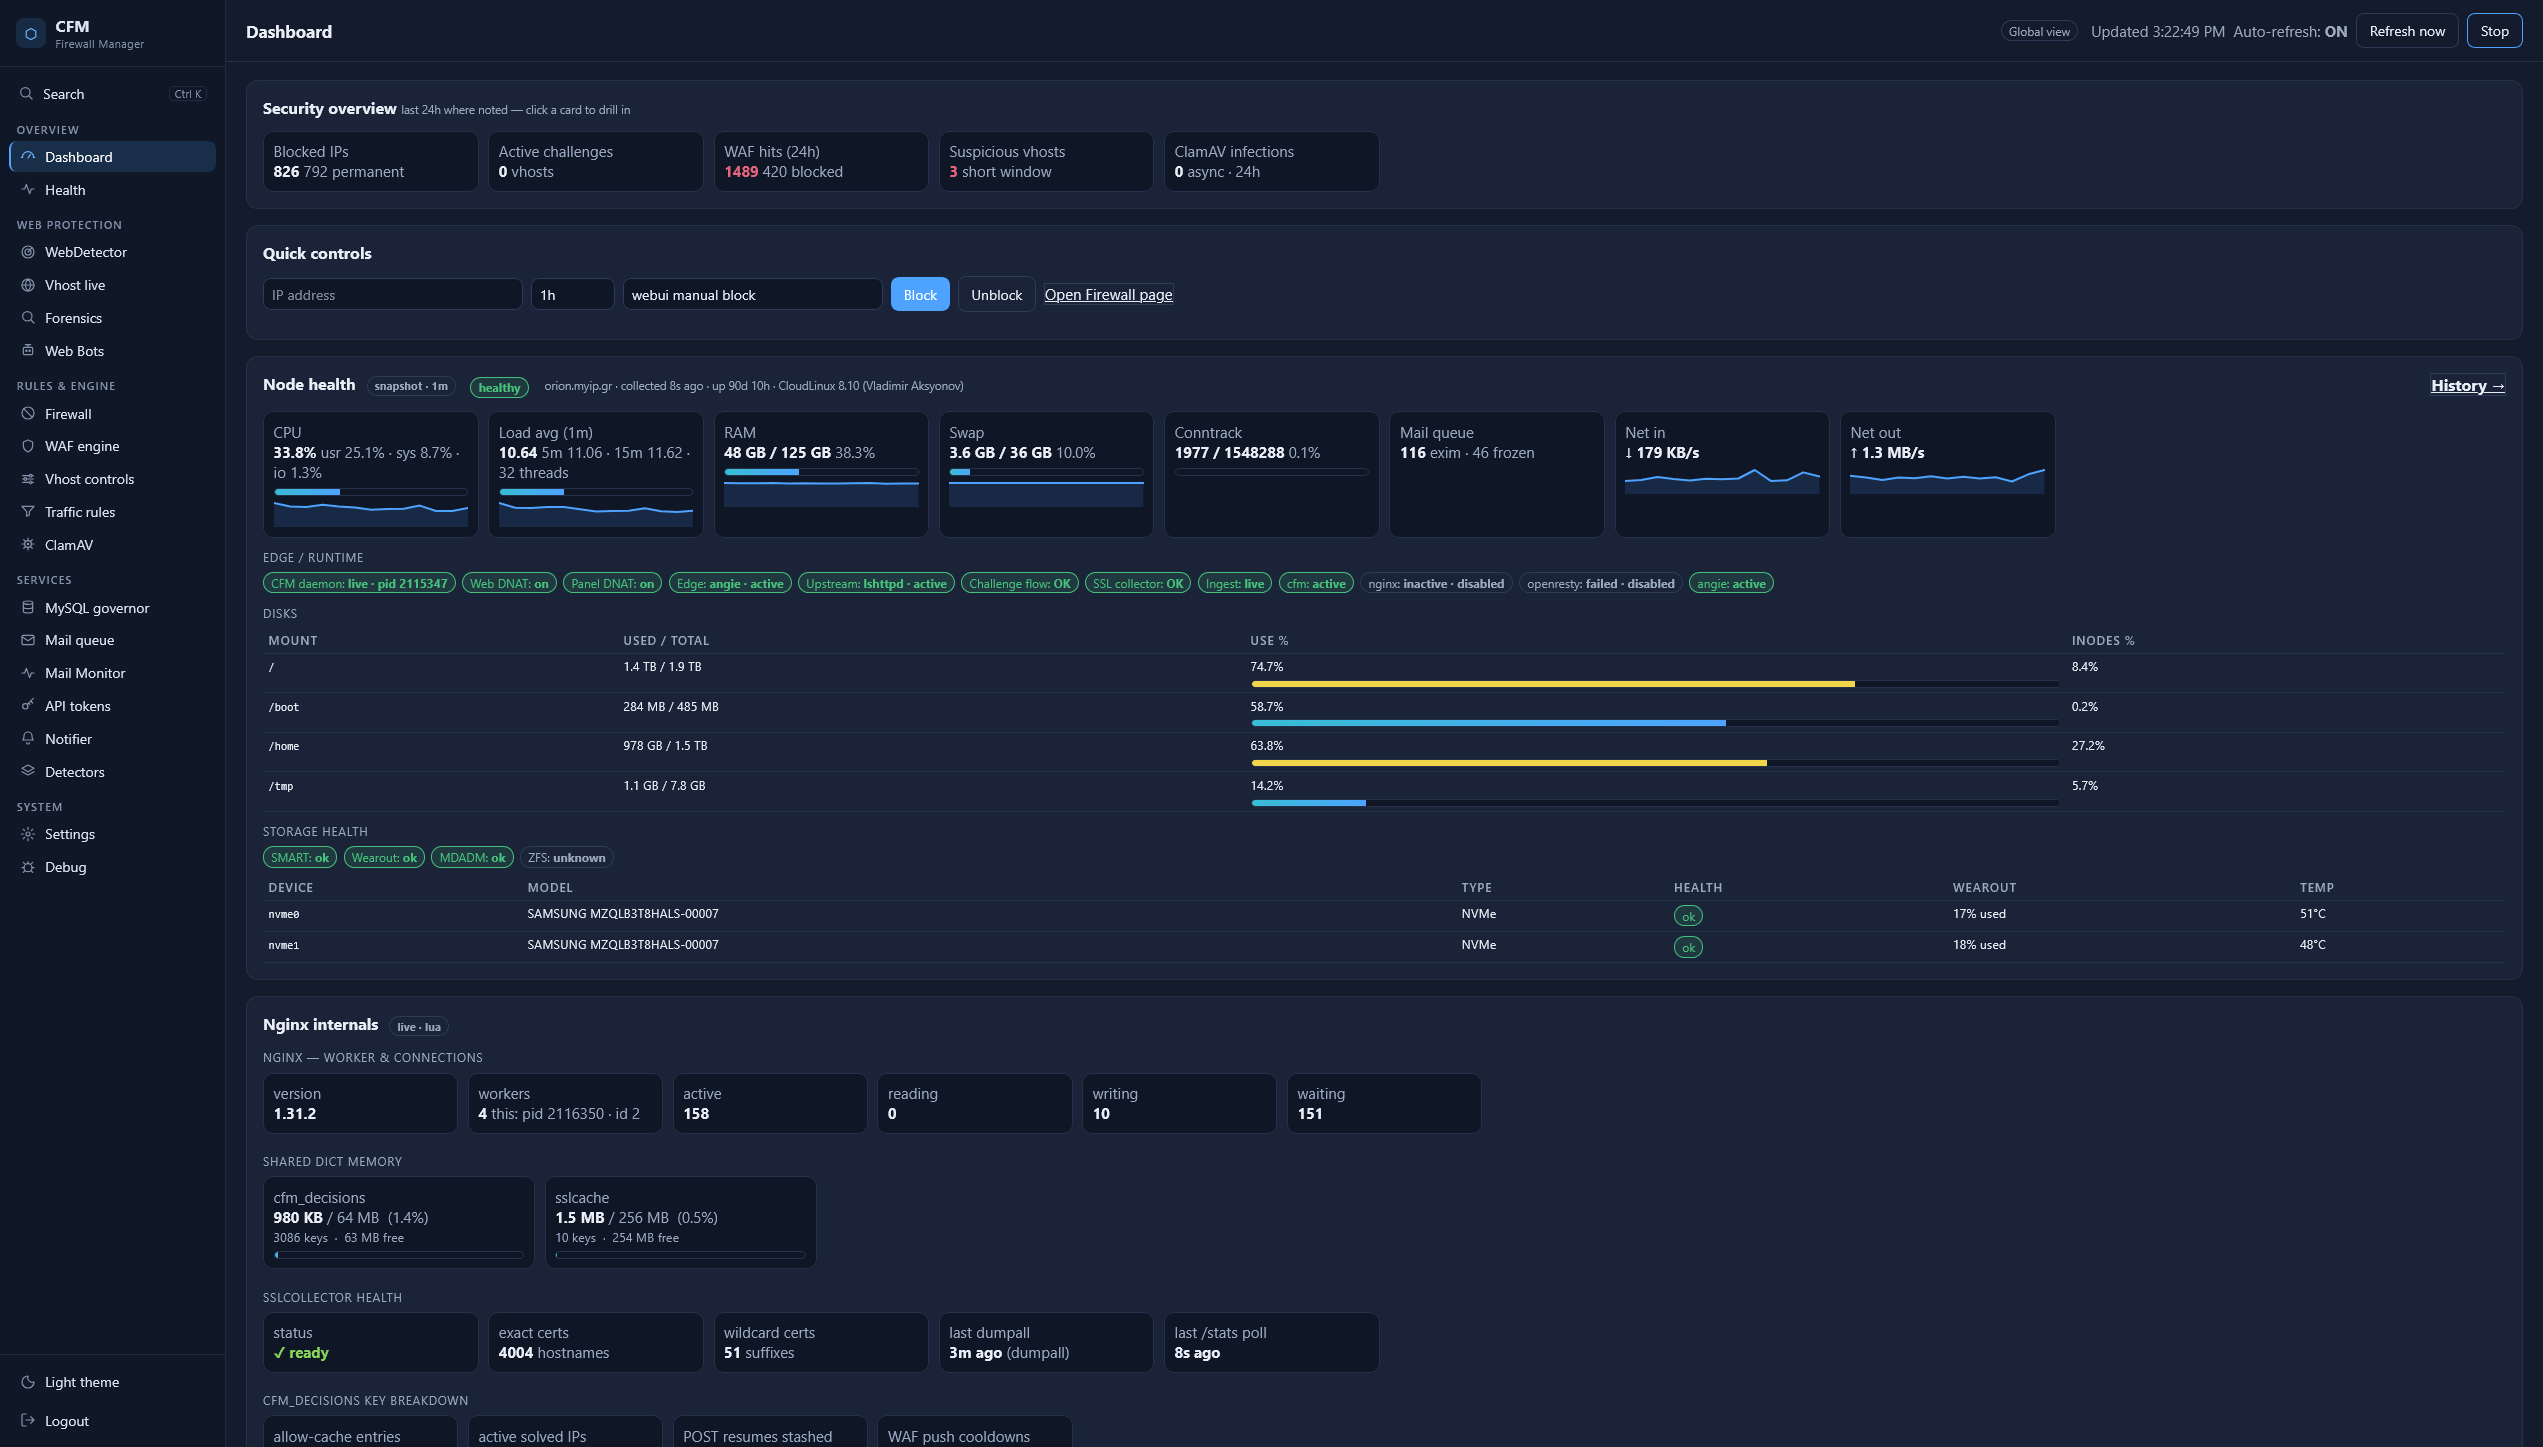
CFM has been CLI-first since day one. This summer it grew a real web UI — and building it turned out to be less about CSS and more about one question: is this page meant to be glanced at, or worked in? Seven lessons, including the dashboard that cost 543 GB of allocations an hour.
CloudLinux says GhostLock has no mitigation. That’s true for the kernel UAF — but not for the public exploit chain. Here’s what CFM already ships against two of its stages, and, just as importantly, what it doesn’t.
BitNinja’s July newsletter — a JavaScript Proof-of-Work CAPTCHA, a unified WAF, and a “coming soon” SOS mode — describes features a one-person, open-source WAF shipped last spring, plus two kernel layers the newsletter never mentions. A friendly, factual comparison.
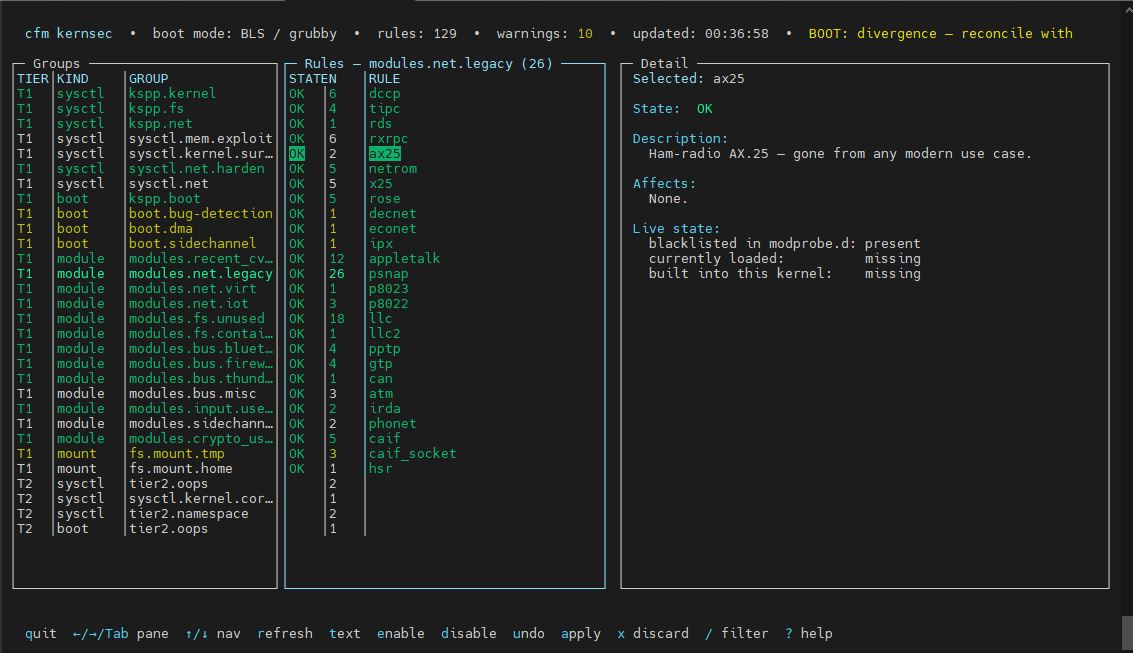
Part of the CFM server security platform. This post covers what kernsec does, how it works, how to use it, and how it relates to the Linux kernel’s proposed Killswitch primitive. The problem it solves A stock AlmaLinux or CloudLinux install ships with a running kernel that supports hundreds of subsystems almost no hosting server … Read more
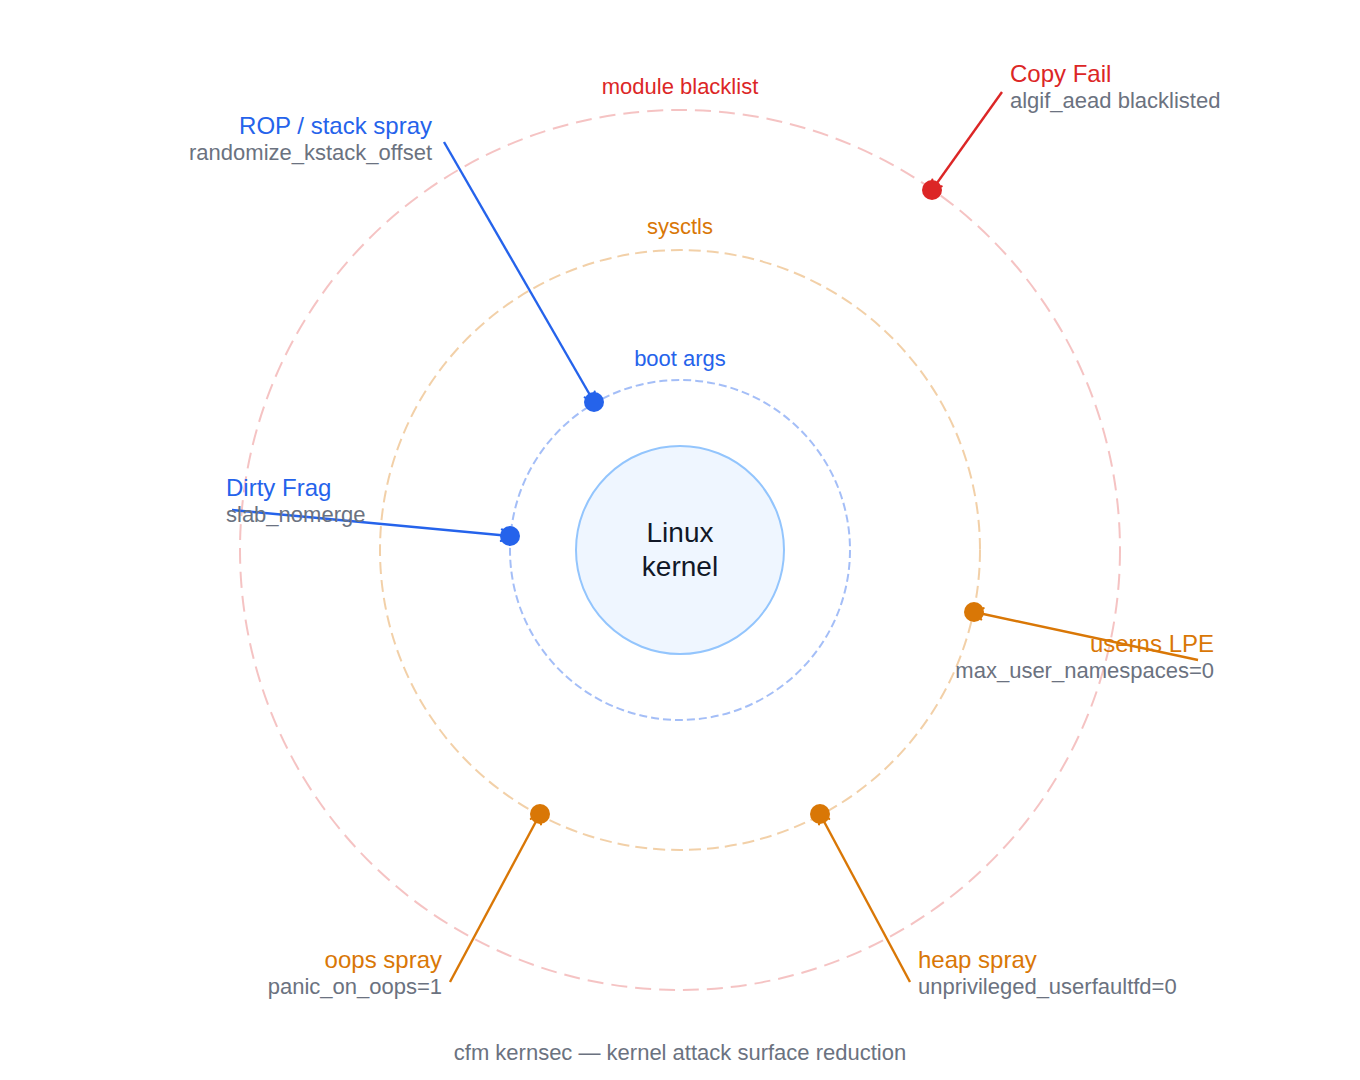
A grounded look at kernel attack surface reduction for production hosting servers — no silver bullets, just honest defense. The kernel LPE wave of 2025–2026 was a good reminder that most Linux servers are running with more attack surface exposed than they need. Dirty Frag, Copy Fail (CVE-2026-31431), the ksmbd parade, watch_queue, Dirty Cred — … Read more
A critical authentication bypass in cPanel & WHM gave attackers root access to over a million publicly exposed servers — silently, without a password, defeating two-factor authentication — for sixty-four days before anyone patched a thing. What Was Actually at Stake cPanel and WHM are not just web applications. They are the administrative nervous system … Read more