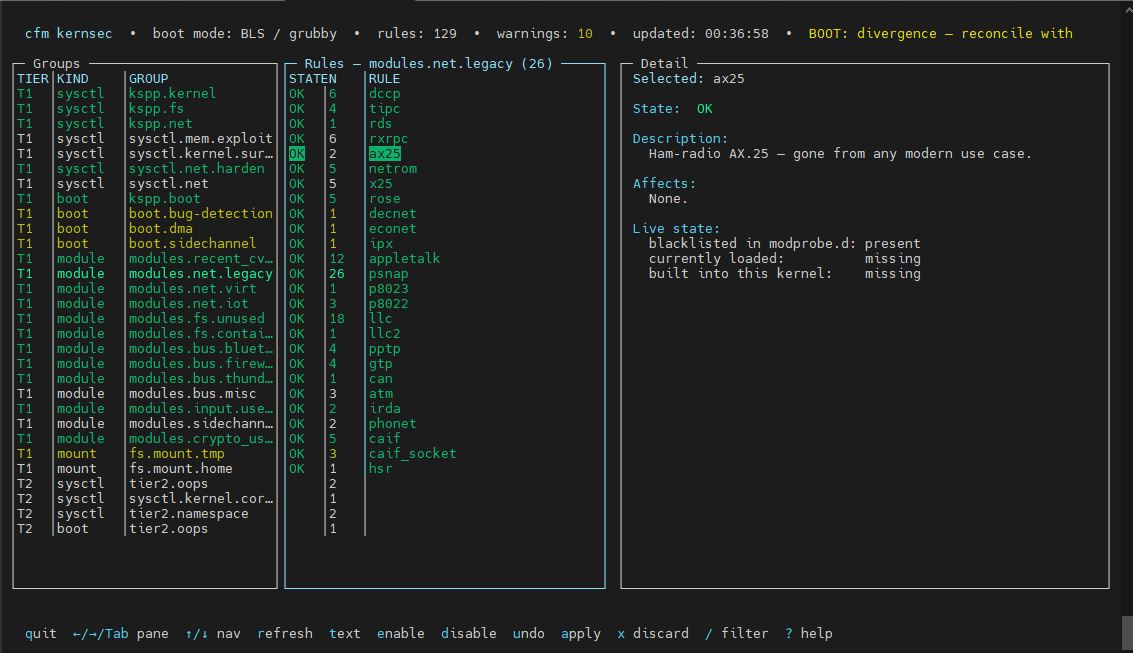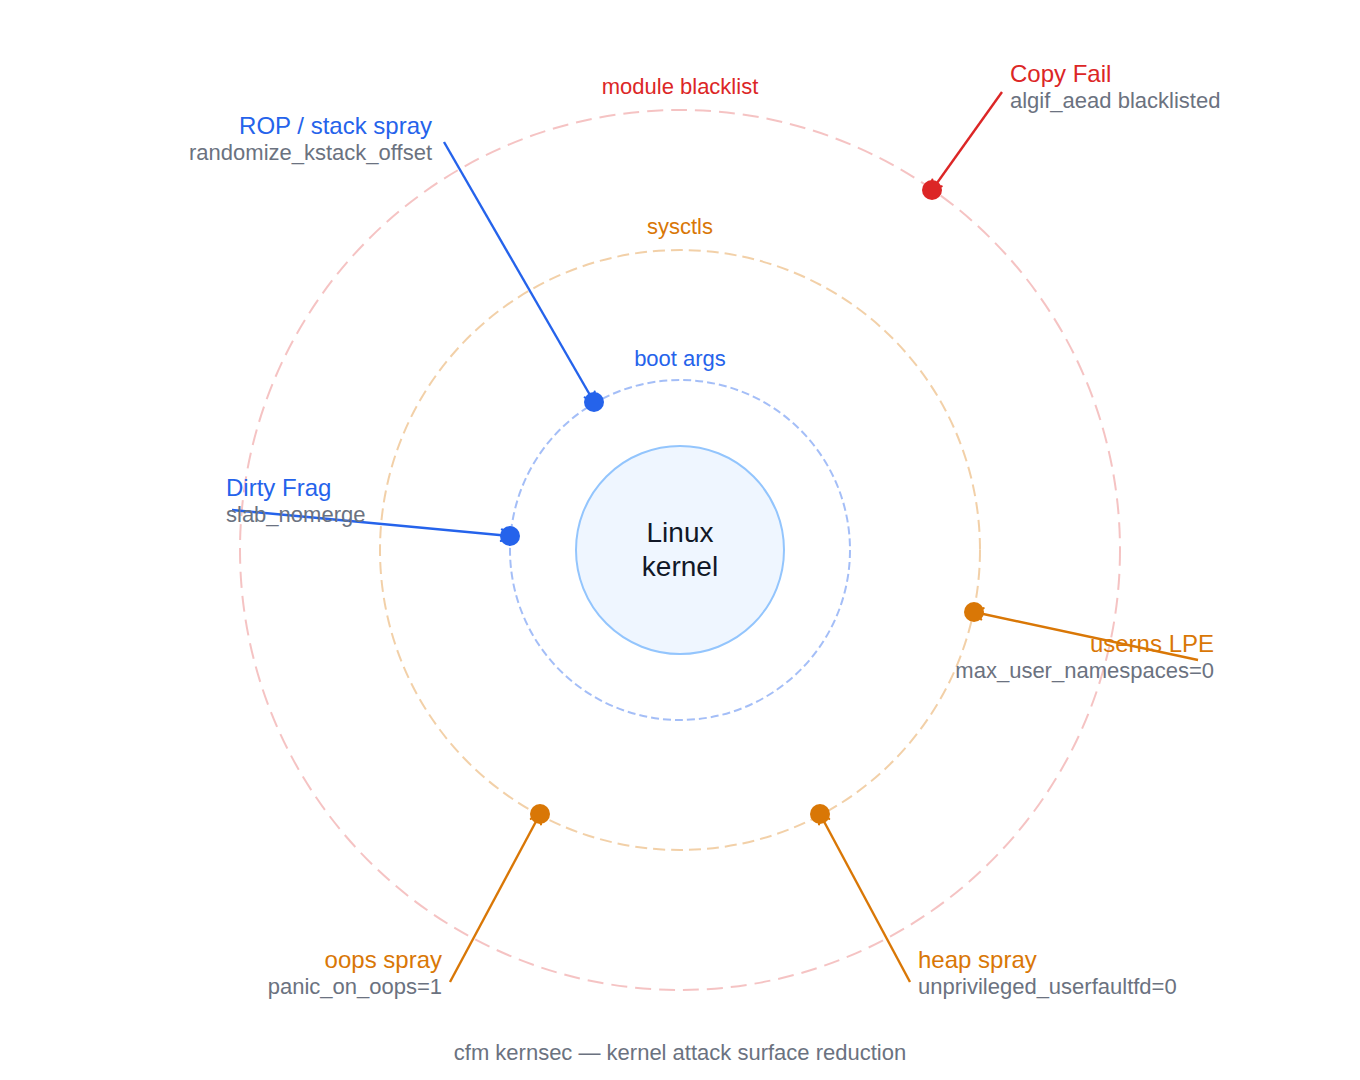
cfm kernsec — Kernel Attack Surface Reduction for Linux

Part of the CFM server security platform. This post covers what kernsec does, how it works, how to use it, and how it relates to the Linux kernel’s proposed Killswitch primitive. The problem it solves A stock AlmaLinux or CloudLinux install ships with a running kernel that supports hundreds of subsystems almost no hosting server … Read more

Hardening Shared Linux Hosting Kernels: What cfm kernsec Actually Does (and Doesn’t Do)

A grounded look at kernel attack surface reduction for production hosting servers — no silver bullets, just honest defense. The kernel LPE wave of 2025–2026 was a good reminder that most Linux servers are running with more attack surface exposed than they need. Dirty Frag, Copy Fail (CVE-2026-31431), the ksmbd parade, watch_queue, Dirty Cred — … Read more

Dealing with igb nic driver dropping network

The problem looks like the device ‘disappears’ from the bus, and becomes inaccessible to the driver. If it happens early – the driver will not load, if it happens later – it may fail with sporadic access errors cat /sys/module/pcie_aspm/parameters/policy grubby –update-kernel ALL –args “pcie_aspm.policy=performance pcie_port_pm=off pcie_aspm=off” dracut -f ethtool -K eno1 tso off gso … Read more